
攻擊面(Attack Surface),指的是系統中所有可能被攻擊者探測、利用或入侵的進入點(Entry points),包含公開的 API、對外開放的 Port、使用者輸入欄位等等...。減少不必要的功能,被駭客利用的破綻就越少,維護成本也會隨之直線下降。
縮小攻擊面的策略
| 策略 | 說明 |
|---|---|
| 減少進入點 (Reduce entry points) | 停用非必要的服務系統,關閉沒有用到的連接埠 (ports) |
| 降低權限 (Reduce privilege) | 讓服務以「滿足需求/剛好夠用」的最低權限來執行 |
| 減少程式碼 (Reduce code) | 刪除並移除沒有用到的死碼 (dead code)、廢棄功能,以及拔除 debug 專用端點 |
| 減少資料儲存 (Reduce data) | 不需要的資料,打從一開始就不要存 |
| 降低信任程度 (Reduce trust levels) | 嚴格限制「是誰」以及「什麼東西」有資格存取各個元件 |
| 網路分段隔離 (Network segmentation) | 將系統各元件隔離打散到各自獨立的網路區段中 |
| API 閘道器 (API gateway) | 透過單一且受到嚴格管控的端點,來集中管理所有的外部存取請求 |
| 策略 | 說明 |
|---|---|
| 白名單/允許清單 (Allowlist / Whitelist) | 僅接受且放行那些符合預先定義好的模式規則之已知安全輸入 |
| 黑名單/拒絕清單 (Denylist / Blacklist) | 攔截並拒絕那些包含已知惡意特徵的輸入 |
| 清洗過濾 (Sanitization) | 將輸入的內容進行清理或轉換,剔除掉危險的部分 |
| 組件 | 說明 | 範例 |
|---|---|---|
| 前置條件 (Preconditions) | 在呼叫該介面之前,什麼條件必須為真 | 輸入參數必須是有效合法的、使用者必須先取得認證 |
| 後置條件 (Postconditions) | 介面執行完畢後,保證能兌現的承諾是什麼 | 資料已被成功加密、稽核日誌已經被確實寫入 |
| 不變條件 (Invariants) | 在該介面的整個生命週期中,某些事物會永遠保持為真 | 帳戶的存款餘額永遠不會是負數 |
Shodan is the world's first search engine for Internet-connected devices. Discover how Internet intelligence can help you make better decisions.
https://www.shodan.io/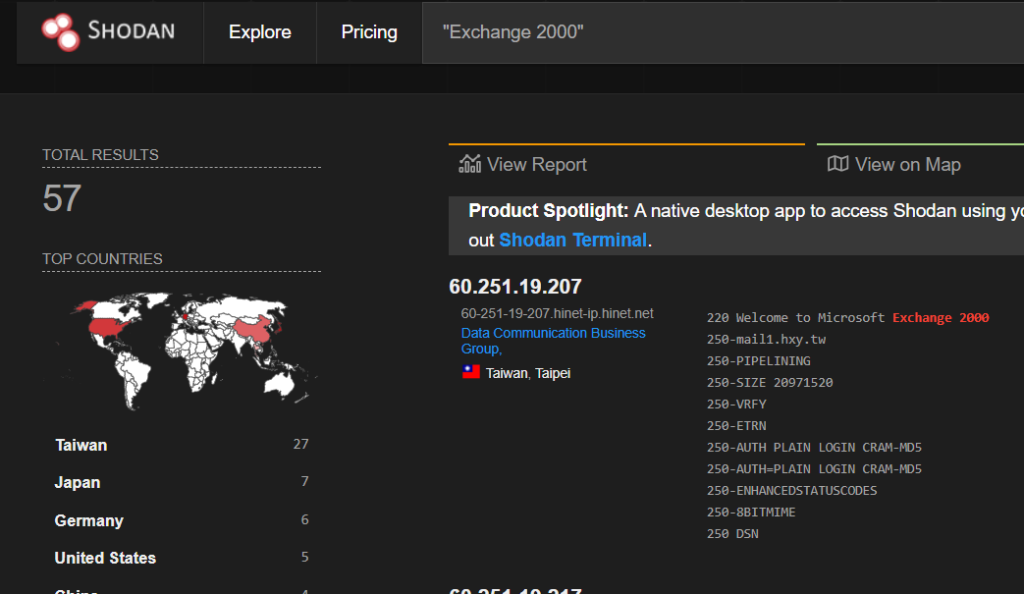
Censys continuously maps internet-facing assets so you can identify risks.
https://censys.com/
Protect your supply chain and manage third-party cyber risk with SecurityScorecard
https://securityscorecard.com/
AI-powered cyber risk intelligence platform. Continuous visibility into your attack surface, third-party ecosystem, and threats.
https://www.bitsight.com/
Panorays is a comprehensive third-party cyber risk management platform, monitoring Risk DNA for early threat detection and proactive defense.
https://panorays.com/


 iThome鐵人賽
 看影片追技術