
前言
前面幾天已經學會了 cd、ls、ls -a 和 cat 等基本 Linux 指令。
今天的 Challenge 則把這些指令全部結合起來,變成一個 Linux 檔案系統的尋寶遊戲。
這次的 Flag 並沒有直接告訴我位置,而是藏在一連串的線索後面。
解題過程需要不斷:
ls 找線索cat 閱讀線索cd
題目:An Epic Filesystem Quest
題目要求從 / 開始。
首先切換到根目錄 /
接著使用 ls
可以看到根目錄中的內容,其中包含
這次並不是直接去讀取 /flag,而是要按照題目的線索一步一步尋找。
首先看到 TIP,因此使用 cat
得到第一個線索 Tubular find!
The next clue is in: /usr/lib/python3/dist-packages/rpyc/core
Watch out! The next clue is trapped. You'll need to read it out without 'cd'ing into the directory; otherwise, the clue will self destruct!
這裡第一次遇到了特殊機制 trapped
題目要求不能 cd 進入這個目錄,否則線索會自毀。
線索告訴我下一個檔案位於 /usr/lib/python3/dist-packages/rpyc/core
一開始如果沒有注意到題目的限制,直接執行 cd /usr/lib/python3/dist-packages/rpyc/core
接著 ls
會看到 LEAD-TRAPPED。
其中 LEAD-TRAPPED 很明顯就是下一個線索。
但因為我已經 cd 進這個目錄,所以再執行 cat
結果得到:
這也讓我真正理解題目的意思,有些線索不能直接進入目錄後再讀取,而必須從外部使用絕對路徑讀取。
因此重新啟動 Challenge 後,再次從 / 開始。
這一次直接使用 cat 加上 LEAD-TRAPPED的路徑
成功取得下一個線索 Tubular find!
The next clue is in: /usr/lib/python3/dist-packages/cryptography/hazmat/primitives/asymmetric/pycache
The next clue is delayed --- it will not become readable until you enter the directory with 'cd'.
這次遇到的關鍵字是 delayed
線索告訴我 /usr/lib/python3/dist-packages/cryptography/hazmat/primitives/asymmetric/__pycache__
而且這次剛好和上一個線索相反。
上一個線索要求不能 cd,這一次則要求必須 cd 進去之後,線索才會變得可以讀取。
首先進入該目錄cd /usr/lib/python3/dist-packages/cryptography/hazmat/primitives/asymmetric/__pycache__
接著 ls
找到 README 後 cat
取得下一個線索 Congratulations, you found the clue!
The next clue is in: /usr/lib/python3/dist-packages/pwnlib/shellcraft/templates/amd64
接著前往 /usr/lib/python3/dist-packages/pwnlib/shellcraft/templates/amd64
使用 ls 找到 DISPATCH 因此cat讀取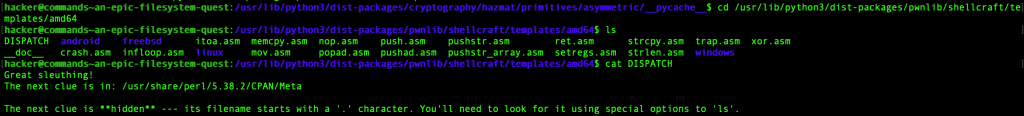
得到Great sleuthing!
The next clue is in: /usr/share/perl/5.38.2/CPAN/Meta
The next clue is hidden --- its filename starts with a '.' character. You'll need to look for it using special options to 'ls'.
這次遇到第三種機制 hidden
也就是下一個線索檔案是隱藏檔案。
ls -a 找隱藏檔案前面 Day 19 已經學過 ls -a
可以顯示以 . 開頭的隱藏檔案。
因此進入指定目錄 /usr/share/perl/5.38.2/CPAN/Meta 接著ls -a 找到 .開頭的檔案
其中 .ALERT 就是隱藏的線索檔案,使用 cat
得到 Lucky listing!
The next clue is in: /usr/lib/x86_64-linux-gnu/perl/5.38.2/auto/mro
前往 /usr/lib/x86_64-linux-gnu/perl/5.38.2/auto/mro
使用 ls 看到 REVELATION 一樣用 cat 讀取 REVELATION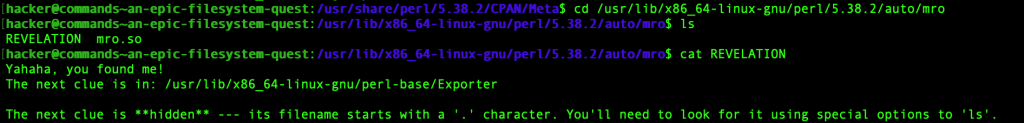
得到下一個線索,這次又遇到 hidden。
所以前往 /usr/lib/x86_64-linux-gnu/perl-base/Exporter
使用 ls -a 找到 .CLUE 接著 cat 它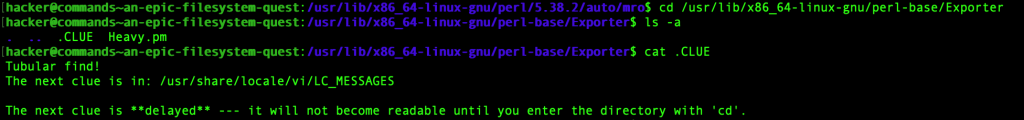
得到下一個線索,而這次又回到 delayed。
前往 /usr/share/locale/vi/LC_MESSAGES
使用 ls 看到 TEASER 因此讀取它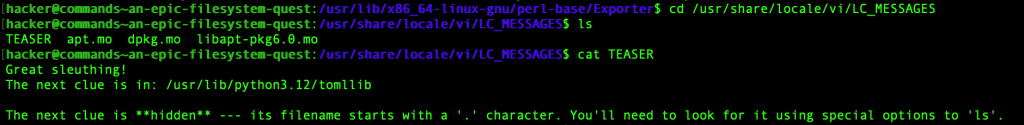
得到下個提示,再次遇到 hidden。
前往 /usr/lib/python3.12/tomllib
使用 ls -a 可以找到隱藏檔案 .HINT 最後使用 cat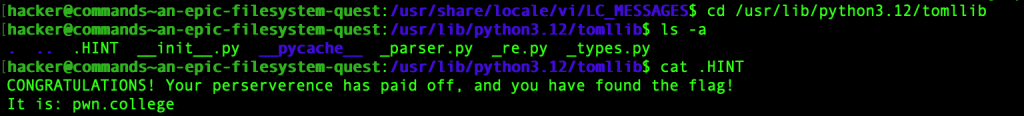
就成功找到 Flag了!
這次 Challenge 最有趣的地方,就是線索本身有不同的限制。
| 類型 | 特徵 | 解法 |
|---|---|---|
trapped |
不能進入指定目錄 | 從外部使用絕對路徑 cat |
delayed |
必須進入目錄後才可讀取 | 使用 cd 進入目錄 |
hidden |
檔案名稱以 . 開頭 |
使用 ls -a 找檔案 |
這三種機制也剛好把前面幾天學到的 Linux 操作全部串了起來。
今天這一題算是目前為止比較有「解謎感」的一題。一開始看到題目時,我原本以為只要一直使用 cd、ls 和 cat 就可以找到 Flag,但實際操作後才發現,線索還有不同的限制。尤其是第一次遇到 trapped 時,我直接 cd 進入目錄,結果線索真的自毀了,只能重新開始。這讓我了解到,在 Linux 環境中,知道指令怎麼使用還不夠,也要仔細閱讀題目提供的資訊與限制,從一開始只是在學單一 Linux 指令,到現在開始利用這些指令解決實際問題,我覺得這也是這幾天學習 Linux 最大的收穫。


 iThome鐵人賽
 看影片追技術