iT邦幫忙

2026 iThome 鐵人賽

DAY 26
0
Security

仿生人是否會夢見網頁山羊? 資安小白的30天Webgoat闖關紀錄系列 第 26 篇

[DAY26]仿生人是否會夢見網頁山羊? --Security Misconfiguration (下)

  • 分享至 

  • xImage
  •  

今天要把剩下的兩部分寫完,也就是執行器端點洩漏(Exposed Actuator endpoints)和加強防護配置(Harden the configuration)
Webgoat A5 Security Misconfiguration 號碼4(題目3)

https://ithelp.ithome.com.tw/upload/images/20261009/20184109MDpcVIbbgc.png

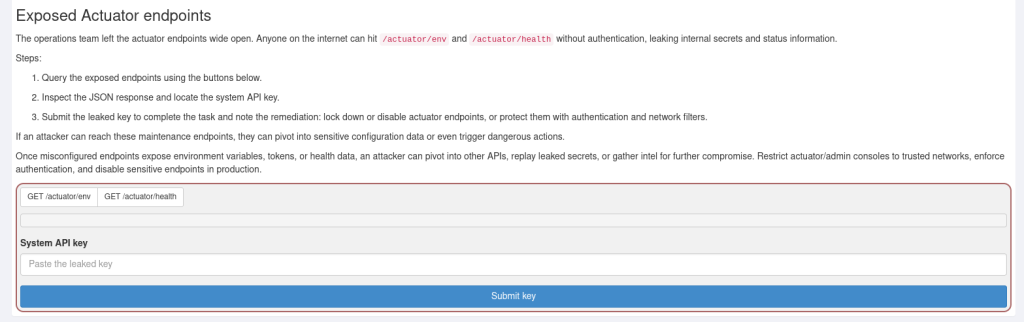
執行器端點洩漏(Exposed Actuator endpoints),指的是開發人員在使用 Spring Boot Actuator 或其他類似管理工具的網頁上線時沒有將監控用的端點(如/actuator/env 和 /actuator/health)開啟權限驗證,從而使攻擊者能夠連結到這些端點獲取資訊,

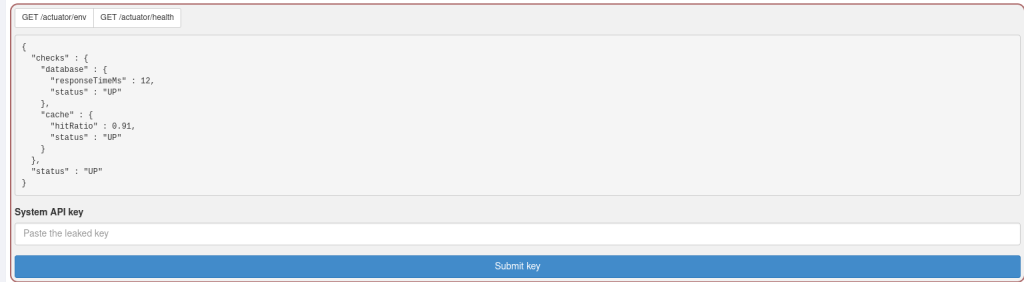
兩個按鈕都按按看,看會有甚麼資訊
https://ithelp.ithome.com.tw/upload/images/20261009/20184109wMSe6JNscV.png

https://ithelp.ithome.com.tw/upload/images/20261009/20184109mXpmgrTJrk.png

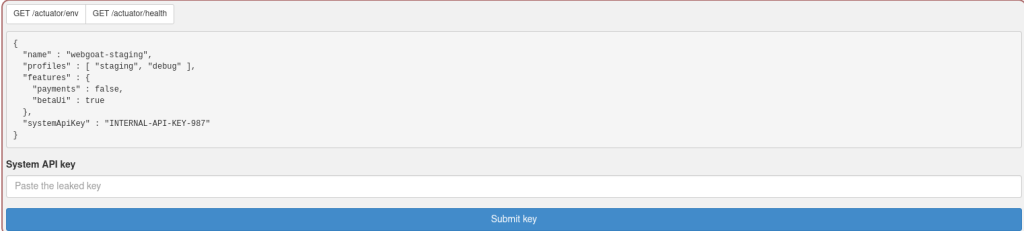
能看到在/actuator/env中不但有這個網頁的功能,還有我們需要的apikey,讓我們輸入進去
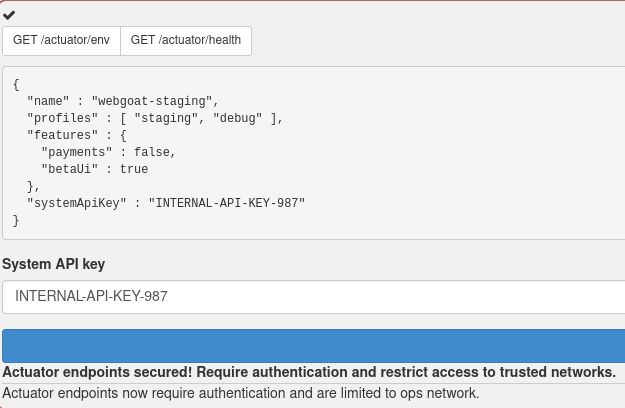
https://ithelp.ithome.com.tw/upload/images/20261009/201841090fajf1v185.png

完成

Webgoat A5 Security Misconfiguration 號碼5(題目4)

https://ithelp.ithome.com.tw/upload/images/20261009/20184109CoywfmZDGs.png

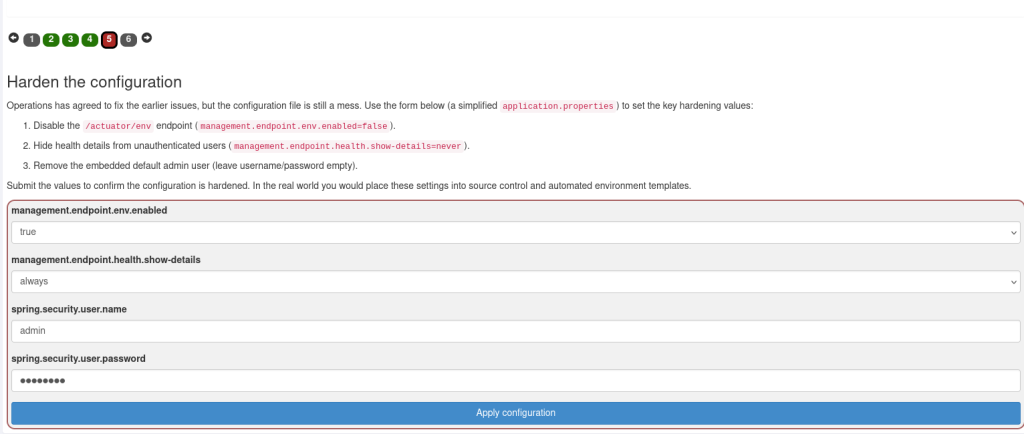
這關就是這小章節的結尾啦,加強防護配置(Harden the configuration),每一步基本上都是對於我們之前提到內容的防護措施
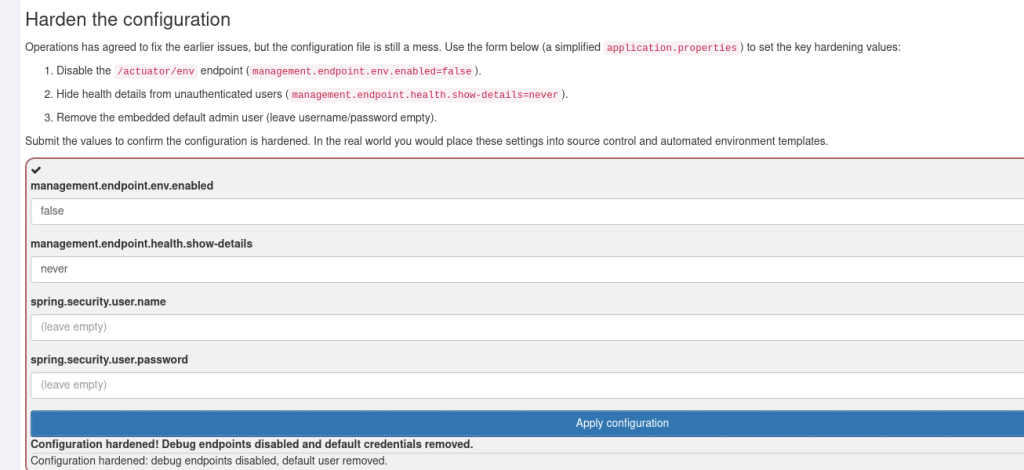
  • management.endpoint.env.enabled=true改為false (關閉執行器端點)
  • management.endpoint.health.show-details=always改為never (避免未經授權的使用者能夠看到詳細報錯資訊)
  • 把username:admin和密碼刪除 (不使用原始用戶名稱以及密碼)

https://ithelp.ithome.com.tw/upload/images/20261009/20184109CgIrnEc8fE.png

明日內容: XXE


上一篇
[DAY25]仿生人是否會夢見網頁山羊? --Security Misconfiguration (上)
下一篇
[DAY27]仿生人是否會夢見網頁山羊? -- XXE (上)
系列文
仿生人是否會夢見網頁山羊? 資安小白的30天Webgoat闖關紀錄 共 30 篇
圖片
  熱門推薦
圖片
{{ item.channelVendor }} | {{ item.webinarstarted }} |
{{ formatDate(item.duration) }}
直播中

尚未有邦友留言

立即登入留言